The EU AI Act (Regulation 2024/1689)
A Breakdown of the Main Rules
Introduction
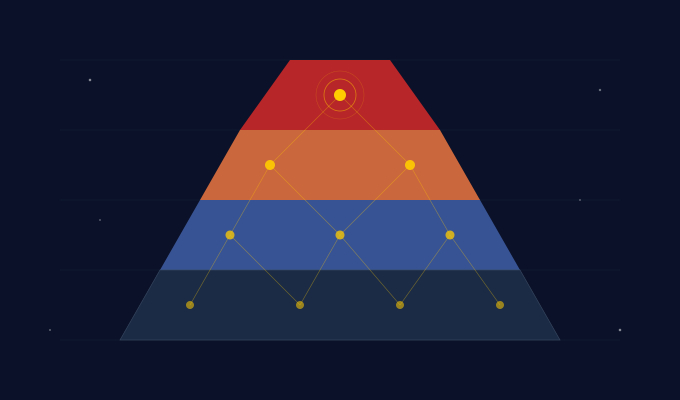
Regulation (EU) 2024/1689, better known as the AI Act, is the European Union's horizontal legal framework for artificial intelligence, and the first comprehensive AI law of its kind in the world. Adopted by the European Parliament and the Council on 13 June 2024, it entered into force on 1 August 2024 and applies in stages rather than all at once. It doesn't regulate AI as a single monolithic category; instead, it builds a risk-based pyramid, scaling legal obligations to how much potential harm a given AI system can cause to health, safety, or fundamental rights.
This post walks through the core rules that matter most for anyone building, deploying, or integrating AI systems that touch the EU market, regardless of where the provider is actually based.
Who It Applies To
The AI Act has broad, extraterritorial reach. It applies to:
- Providers placing AI systems or general-purpose AI (GPAI) models on the EU market, regardless of where they are established.
- Deployers of AI systems located within the EU.
- Providers and deployers located outside the EU, if the output produced by their AI system is used within the Union.
- Importers, distributors, and certain other actors in the AI value chain.
In short: if your AI system's output reaches EU users or EU markets, the Regulation can reach you, even if your company has no EU presence.
The Risk-Based Pyramid
The core structure of the Regulation is a four-tier classification system. The higher the potential risk to people, the stricter the obligations.
1. Unacceptable Risk: Prohibited Outright (Article 5)
A small set of practices are banned across the EU, regardless of sector or claimed justification, including scientific research. Article 5 prohibits eight categories of AI practice:
- Subliminal, manipulative, or deceptive techniques that materially distort a person's behavior and cause significant harm.
- Exploiting vulnerabilities linked to age, disability, or social/economic situation to distort behavior harmfully.
- Social scoring by public or private actors that leads to detrimental or disproportionate treatment unrelated to the context in which the data was generated.
- Predicting an individual's risk of committing a crime based solely on profiling or personality traits, without objective, verifiable facts.
- Untargeted scraping of facial images from the internet or CCTV footage to build or expand facial-recognition databases.
- Emotion inference in workplaces and educational institutions, except for narrow medical or safety purposes.
- Biometric categorization used to infer sensitive attributes such as race, political opinion, trade union membership, religion, or sexual orientation.
- Real-time remote biometric identification in publicly accessible spaces for law enforcement, permitted only for three narrowly defined purposes (searching for victims of trafficking or missing persons, preventing an imminent terrorist threat, or locating a suspect in specific serious crimes), and only with prior judicial or independent administrative authorization.
These prohibitions have already been enforceable since 2 February 2025.
2. High Risk: Strict Obligations (Chapter III)
High-risk systems are those listed in Annex III (e.g., employment and worker management, access to essential public and private services, education, biometrics, law enforcement, migration and border control) or that act as a safety component of products already regulated under EU product-safety law (Annex I: medical devices, machinery, aviation, and similar).
Providers of high-risk systems must implement:
- A risk management system spanning the entire lifecycle of the AI system.
- Data governance measures to ensure training, validation, and testing datasets are relevant, representative, and free of errors to the extent feasible.
- Technical documentation and automatic logging capabilities to ensure traceability.
- Transparency and instructions for use that allow deployers to operate the system correctly.
- Human oversight measures, so a natural person can effectively monitor and intervene.
- Accuracy, robustness, and cybersecurity requirements appropriate to the system's intended purpose.
- A conformity assessment before the system is placed on the market, plus registration in an EU database for standalone Annex III systems.
Deployers of high-risk systems also carry obligations, including monitoring the system's operation, ensuring input data is relevant, and, in specific public-sector or high-impact contexts, conducting a fundamental rights impact assessment.
3. Limited Risk: Transparency Obligations (Article 50)
Systems that interact directly with people or generate synthetic content must meet disclosure requirements, even if they don't qualify as high-risk. This covers chatbots and conversational AI (users must be informed they're interacting with an AI system), and generative or manipulated content such as deepfakes (which must be clearly labeled as AI-generated or manipulated).
4. Minimal Risk: No Specific Obligations
The largest category by volume, including spam filters, AI-enabled video game features, and recommendation systems without a significant risk profile, carries no mandatory obligations under the Act, though providers are encouraged to adopt voluntary codes of conduct.
General-Purpose AI (GPAI) Models
The Regulation carves out a separate regime for general-purpose AI models: the large foundation models that underpin many downstream applications. Since 2 August 2025, providers of GPAI models must maintain technical documentation, provide information to downstream providers integrating the model, put in place a policy to respect EU copyright law, and publish a sufficiently detailed summary of the content used for training.
Models classified as carrying systemic risk (currently determined largely by a compute threshold) face additional obligations: model evaluation, adversarial testing, tracking and reporting serious incidents, and ensuring adequate cybersecurity protection.
Penalties
The AI Act backs its obligations with a tiered fine structure, calculated as whichever is higher between a fixed amount and a percentage of global annual turnover:
| Violation Type | Maximum Fine |
|---|---|
| Breach of prohibited-practice rules (Article 5) | €35 million or 7% of global turnover |
| Breach of other obligations (e.g., high-risk requirements) | €15 million or 3% of global turnover |
| Supplying incorrect, incomplete, or misleading information to authorities | €7.5 million or 1% of global turnover |
A Recent Development: The Timeline Has Shifted
It's worth flagging that the original implementation calendar has changed. Facing concerns over the pace of technical standards and compliance readiness, the European Commission proposed a "Digital Omnibus on AI" in November 2025 to delay parts of the schedule. That proposal has since been finalized: the European Parliament and Council reached political agreement in May 2026, and formal approval followed in June 2026. As a result, the applicability dates now look like this:
| Milestone | Original Date | Current Date |
|---|---|---|
| Prohibited practices (Art. 5) apply | 2 Feb 2025 | 2 Feb 2025 (unchanged) |
| GPAI model obligations apply | 2 Aug 2025 | 2 Aug 2025 (unchanged) |
| High-risk obligations, Annex III (standalone systems) | 2 Aug 2026 | 2 Dec 2027 |
| High-risk obligations, Annex I (embedded/product-safety systems) | 2 Aug 2027 | 2 Aug 2028 |
Transparency obligations under Article 50 remain on the original August 2026 schedule for deployers, though certain watermarking obligations on providers have been pushed to December 2026. The underlying architecture of the Act (the risk tiers, the prohibited-practice list, and the GPAI rules) hasn't changed; what shifted is how much runway organizations have before the high-risk regime becomes fully enforceable.
Conclusion
The AI Act doesn't try to regulate "AI" as an abstract concept; it regulates specific uses and their potential to harm people, scaling obligations accordingly. For most organizations building on top of foundation models or deploying AI in regulated or sensitive contexts, the practical takeaway is the same regardless of the exact compliance date: risk classification comes first. Knowing whether a given system falls into the prohibited, high-risk, limited-risk, or minimal-risk tier determines everything else, including documentation, oversight, transparency, and exposure to fines, and given how much the implementation timeline has already moved once, it's a classification worth revisiting periodically rather than doing once and filing away.
Sources
- Regulation (EU) 2024/1689, EUR-Lex (official text)
- Article 5 (Prohibited AI Practices), CASRAI Dictionary
- Prohibited AI Practices: A Deep Dive into Article 5, WilmerHale (via JD Supra)
- EU AI Act Risk Categories: The 4 Tiers Explained, Jaggaer
- The Artificial Intelligence Act, Beauchamps
- An Analysis of the EU AI Act, BDO Malta
- EU Lawmakers Reach Provisional Agreement to Delay Key EU AI Act Obligations, Sidley
- EU AI Act Omnibus Agreement: Postponed High-Risk Deadlines and Other Key Changes, Gibson Dunn
- EU Legislators Agree to Delay for High-Risk AI Rules, Hogan Lovells
- AI Act Rules on High-Risk AI Delayed as AI Digital Omnibus Agreed, Winston & Taylor